
Most NIS2 obligations have a playbook. Supply chain security doesn't.
Vittnor — Supply Chain Assurance for the mid-market. It turns supplier proof into structured, audit-ready records — without the spreadsheet sprawl. Built in central Europe for the buyers that bigger players ignored, by a team led by a cybersecurity practitioner who's been in your shoes.
- Pilot free for the first cohort
- EU-built, EU-hosted
- Audit-ready evidence records
- No tracking cookies
 Enlarge
Walk through the NIS2 obligations as a CISO or Head of IT. Awareness training has a playbook. Incident response has a runbook. Patch management is procedural. Supply chain security isn't. The evidence sits with external parties. It arrives in a dozen formats. It expires unevenly. And someone has to defend the decisions later. That's why Vittnor is its own product — because the obligation deserves its own tool.
Structured supplier evidence — without the spreadsheet sprawl.
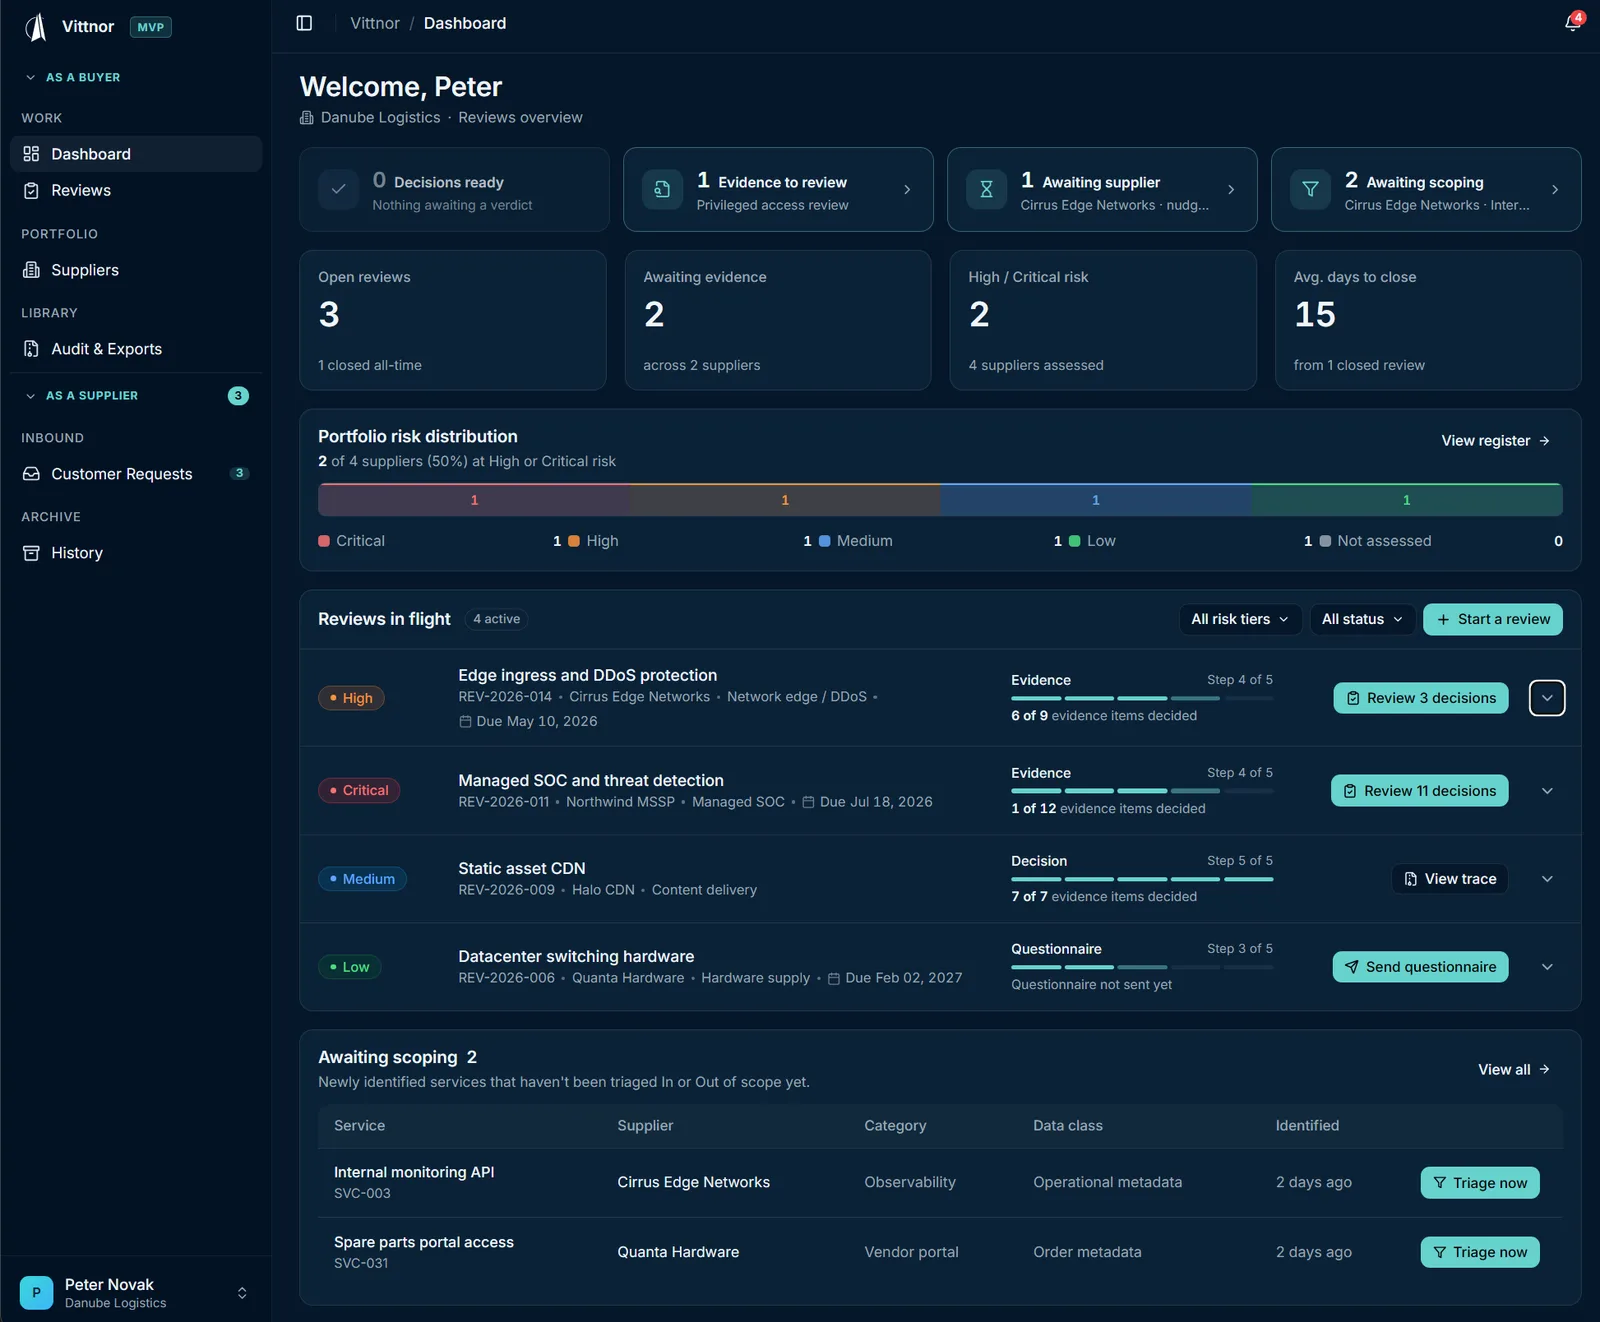
Vittnor turns supplier proof — certificates, audit reports, contract clauses, policy documents — into Evidence records with expiry context and a full decision trace. When a supplier has an incident, an auditor asks a hard question, or a regulator sends an inquiry, you have the answer in minutes, not hours.
- Process-driven supplier scoping
- Structured risk assessment — a tier for each of six categories
- Evidence records with review history
- Review decisions per supplier and period, with an audit log of who did what
Stored in the EU — Microsoft Azure, Sweden Central.
Read the long-formFull list, updated on every change. DPA template available before the deal.
Read the long-formHash-anchored, signed, decision-traced. Stands up six months later, unchanged.
Read the long-formWhen a supplier discloses an incident.
One scenario. Two ways it goes. The difference is what you signed up for the day before it happened.
Open the supplier register spreadsheet. Search SharePoint for their last assessment, your inbox for the contract clauses, a different folder for the evidence files, your calendar for the last review date. Half a day per supplier. Longer if the original reviewer has left. By the time you've reconstructed who reviewed what and when, you're not sure you have the latest version of anything.
One record per supplier. Current evidence, review history, contract clauses, in-scope services — linked, dated, exportable. The CEO gets the answer the same morning. The auditor gets the same answer six months later, unchanged.
What you actually get.
Evidence, decisions, exports — the three things an auditor actually asks for. We build supplier-assurance tooling and we're honest about what it's for: no 24/7 SOC, no managed endpoint agents.
How it fits togetherSub-processor lists, certificates, audit reports — linked, dated, with reviewer attribution. Always the latest version.
Every approval and rejection recorded with who made it and when. Auditor asks "why was that rejected" — the answer is on file.
Who uploaded what, who reviewed it, who decided — recorded as it happens.
Pavel Láska.
I did this work before we built the tool for it.
I spent eight years in banking, on critical financial infrastructure, working up from senior engineer to senior risk manager. Then I managed a global security services team in pharma, across three continents.
Along the way, I was the person filling in the supplier spreadsheets, writing the risk assessments that went up to board committees, and preparing the evidence packs for auditors.
At audit time, everything else got dropped. The hard part was never proving compliance. It was finding what we already had, in the right form, before the auditor's next question. Vittnor is for whoever does that work now.
Backend and frontend engineers build Vittnor, with operations, cyber compliance and sales working alongside them.
Handled by a qualified ISO 27001 Lead Auditor.

The architecture was tested against Microsoft's own standards.
Shaped in conversations with people on both sides of the audit: CISOs, IT security managers and auditors.
Two ways to start. Both open today.
Run your supplier register in Vittnor — free for the first cohort of design partners. You shape what ships; V1 lists on the Microsoft Marketplace Q4 2026.
Start with the NIS2 Supplier Exposure Assessment — fixed scope, fixed deliverable, €3,900 one-off. A practitioner-written report on where your supplier risk actually sits, in two to three weeks. Or try the free five-minute readiness check first →
A ten-minute form about your company and suppliers. You hear back from the founder personally.
Thirty minutes on your supplier register and what the pilot should prove for you.
Your first suppliers in Vittnor within two weeks.
Pilot open today. Free for the first cohort.
We help you, you help us — the first cohort shapes what we build next. After the pilot: a Free plan, and a paid plan through the Microsoft Marketplace. See pricing →
Nothing to install, no credit card, no procurement cycle — the pilot runs on your real supplier register in Vittnor.